Bypassing Snort Signature Detection
Introduction Most of today’s corporations rely on hybrid protection mechanisms to deal with threats and recognize their patterns. One of these assets in network security is known as IDS/IPS (Intru...
Introduction Most of today’s corporations rely on hybrid protection mechanisms to deal with threats and recognize their patterns. One of these assets in network security is known as IDS/IPS (Intru...
Introduction In today’s digital era, various tools and frameworks are built to satisfy the needs of IT administrators and solve operative issues. As an example, most tasks in corporations require ...
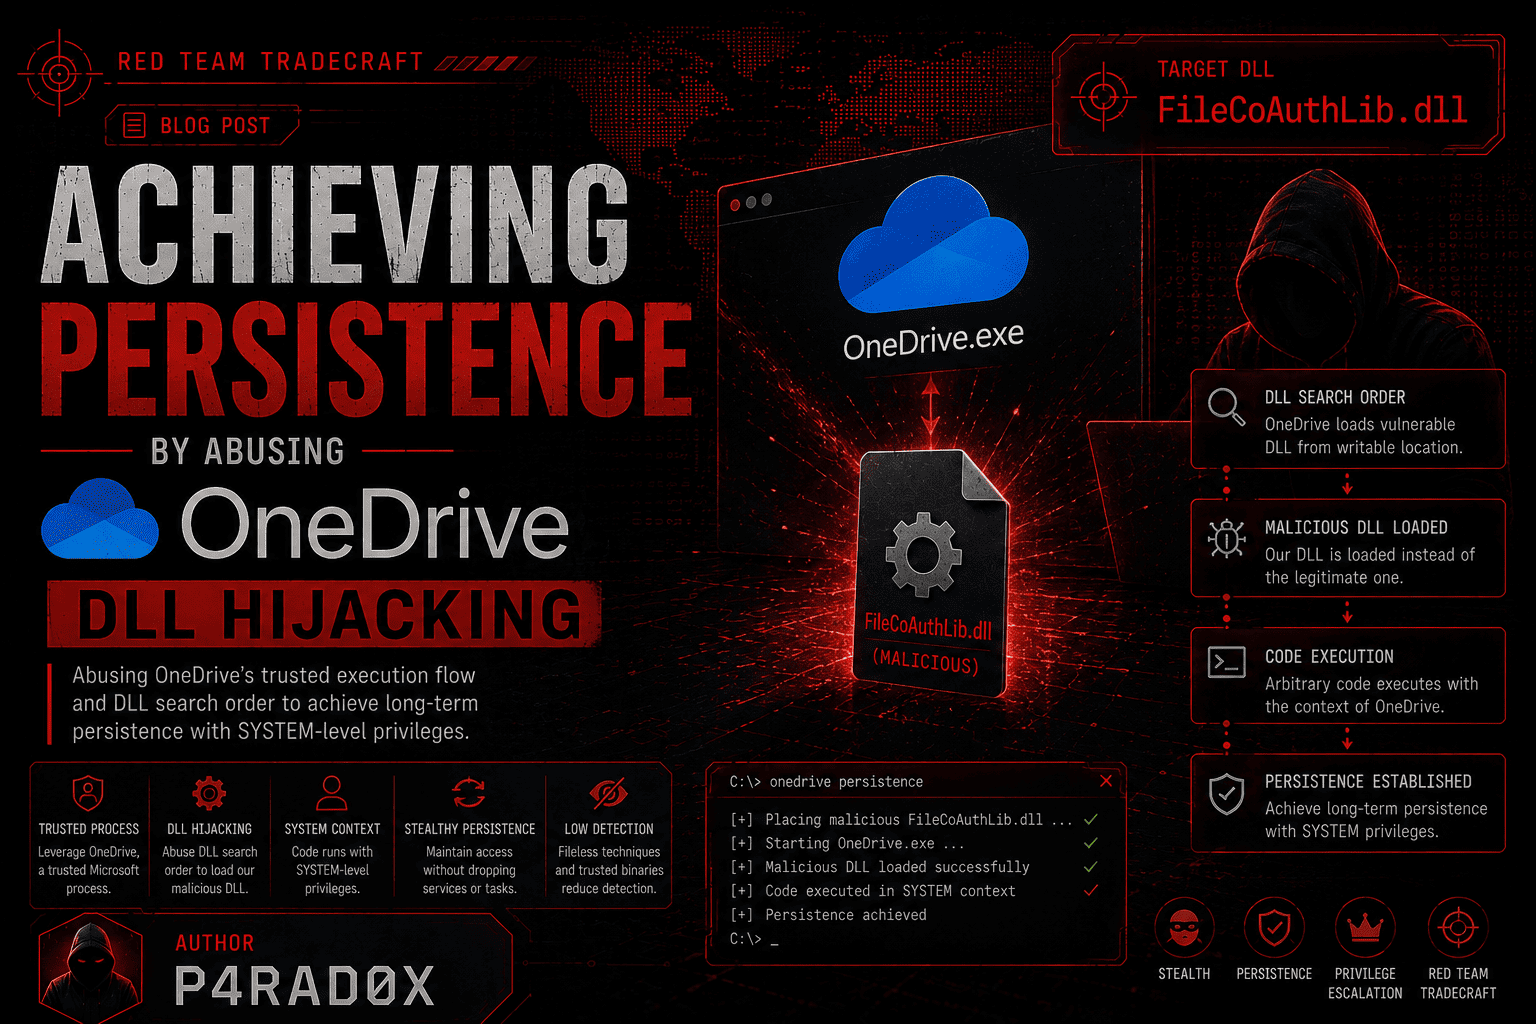
Introduction When discussing post-exploitation tradecraft, persistence is one of the most critical phases in any adversary kill chain. Gaining initial access is only half the battle — maintaining ...
Introduction Throughout this article, we’ll be examining one of the most common yet hazardous techniques adversaries employ to deliver their payloads and establish reliable access to their targets...
Introduction : In this article, we’re going to be exploring one of the common attack vectors in adversary scenarios. The core concept of this technique relies on social engineering and payload exe...